
AutoTableTop
FortiBleed Credential Compromise
In June 2026, independent researchers disclosed FortiBleed, a large-scale credential-harvesting campaign that exposed verified administrator and VPN credentials for more than 86,644 internet-facing Fortinet FortiGate devices across 194 countries. Unlike a conventional zero-day,

Summary
In June 2026, independent researchers disclosed FortiBleed, a large-scale credential-harvesting campaign that exposed verified administrator and VPN credentials for more than 86,644 internet-facing Fortinet FortiGate devices across 194 countries. Unlike a conventional zero-day, FortiBleed carries no single CVE number - it is the product of weak legacy password hashing inherited from pre-2025 FortiOS versions, compounded by years of credential reuse traceable in part to earlier exploitation of CVE-2024-21762 and related Fortinet vulnerabilities.
ManufcaturingCo is a fictional composite organization created specifically for this exercise. While the FortiBleed campaign itself — the timeline, attribution, CVE history, and CISA/NCSC advisories — is drawn from real, publicly reported incident data, the target company, its personnel, network architecture, and specific intrusion narrative are invented for tabletop exercise purposes. We built this scenario around a fictional target rather than one of the real organizations named in the FortiBleed disclosures because the exercise requires fabricated internal detail, including staff names, network topology, and specific response decisions, that would be inappropriate to attribute to an actual company that was genuinely affected.
ThreatGEN built this scenario around a representative composite organization, ManufcaturingCo (a fictional company), a $4.2 billion specialty metals and aerospace-components manufacturer with FortiGate appliances at all 42 of its global facilities. The exercise opens at the exact moment IMG learns that one of its own administrative credentials has surfaced in the leaked FortiBleed corpus and follows a real intrusion as it unfolds through that exposure, reaching toward ManufcaturingCo's OT-adjacent vendor-support environment before containment.
- 86,644 Devices Exposed
- 194 Countries Affected
- 45-GPU Cracking Cluster
- 0 Malware Files Used
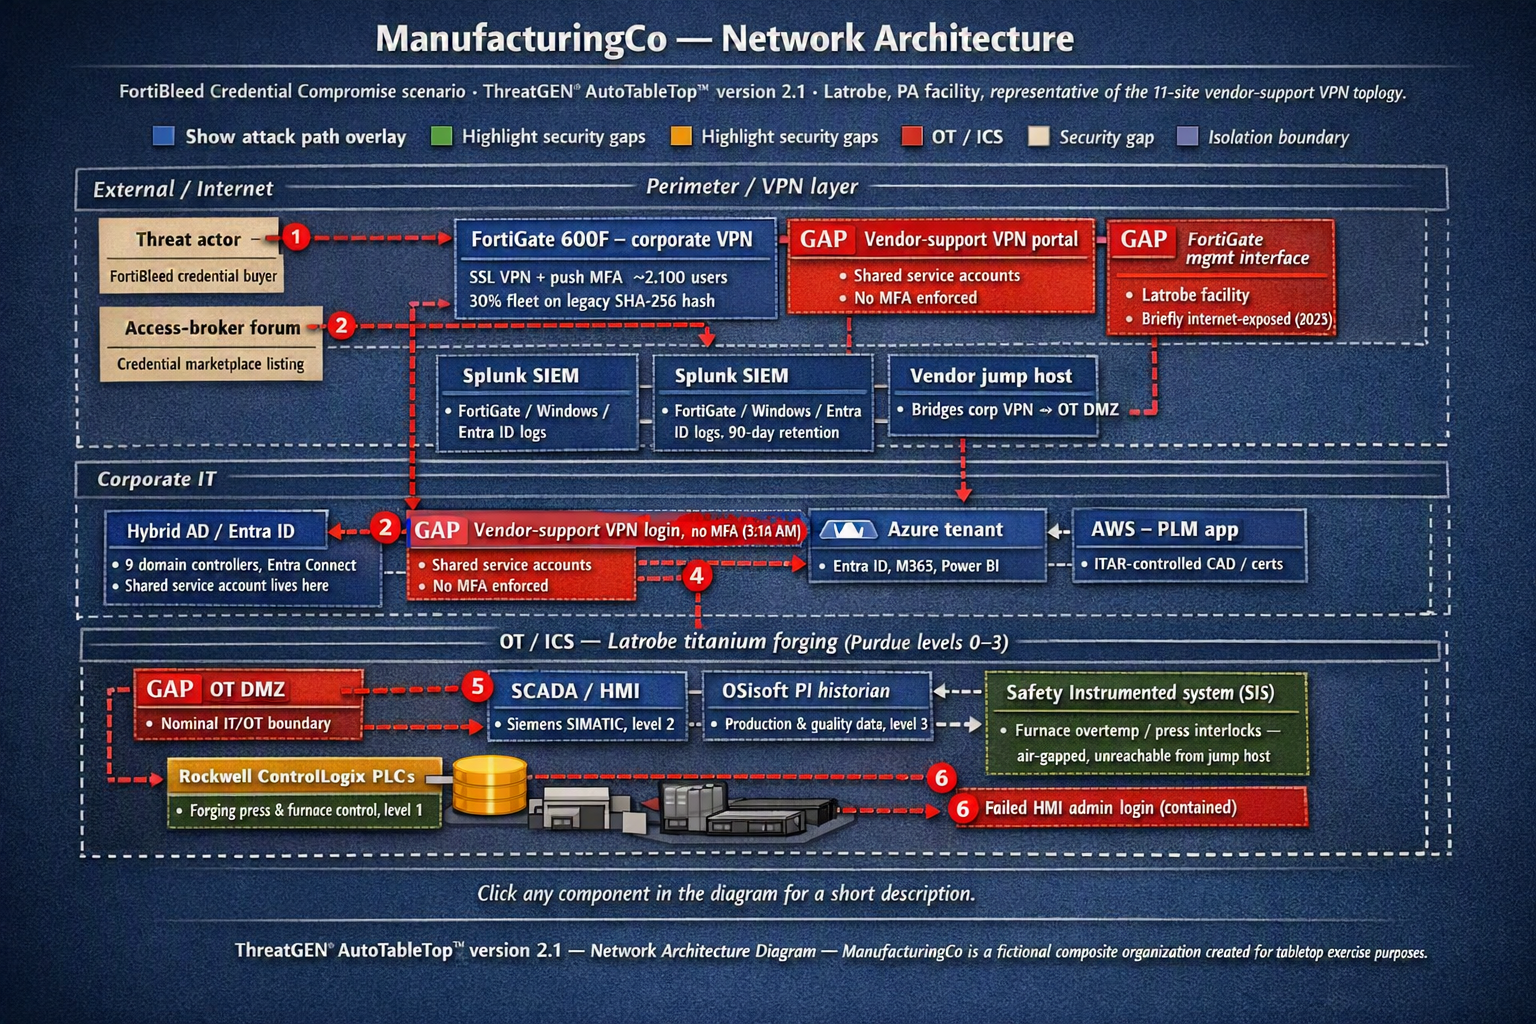
ThreatGEN provides a complete exercise package for AutoTableTop™ version 2.1 facilitators to run tabletop exercises based on this scenario. The package includes a Settings File with a detailed network environment, and six scenario injects, a Facilitator Guide, a Participant Presentation, an interactive Network Architecture Diagram, and a sample Incident Response Plan — all grounded in publicly available reporting on the real-world FortiBleed campaign.
Why This Scenario Matters
FortiBleed inverts the usual incident-response starting point. Most playbooks begin with "we detected an intrusion" and work backward to the entry point. Here, the entry point was disclosed publicly before any intrusion was detected, and the organization learned its own credential was sitting in a criminal database days before an attacker used it. This is deliberately not a ransomware scenario: there is no ransom note, no encryption event, and no negotiation channel. The pressure is different in kind - a race against an active access-broker marketplace listing, layered with defense-industrial compliance deadlines (DFARS 7012, CMMC, ITAR) that run independently of the technical response.
Exercise Themes
Credential vs. Ransomware Response
Distinguishing a credential-compromise incident from a ransomware incident and adjusting posture accordingly.
Legacy Hashing Exposure
Why upgrading FortiOS alone doesn't close the gap without a completed hash migration.
MFA Exemption Risk
How a "vendor support" MFA carve-out becomes the weakest link in an otherwise strong posture.
IT/OT Segmentation Failure
How a single shared service account can bridge segments believed to be isolated.
Access-Broker Escalation Risk
Treating a marketplace listing as an urgent detection signal, not passive threat intel.
DFARS / CMMC / ITAR Pressure
Parallel, fast-moving defense-supply-chain compliance deadlines.
Disclosure Control
Responding when a public breach-lookup tool outpaces your own investigation timeline.
Threat-Intel Notification SLAs
Defining a fast internal response window for third-party leaked-credential alerts.
OT Isolation Decision-Making
Weighing production impact against containment urgency in real time.
Scenario Package Files
This scenario is available as a global scenario within the AutoTableTop™ version 2.1 interface. The scenario files available here are:
- Facilitator Guide (PDF) - Guide with threat actor profile, full attack chain and timeline, MSEL, injects, and scoring rubric.
- FortiBleed presentation (PDF) - Presentation for tabletop participants briefing them on the incident and salient points to enhance the exercise.
- Network Diagram (PDF) - A network diagram with attack path overlay.
- I/R Plan (PDF) - A sample incident response plan assuming IMG as the basis for the plan. The plan includes individuals that were part of the plan during real life.
- Settings File (JSON)- This is the JSON settings file used within the global version 2.1 interface.
Available as a Built-In Template
This scenario is available as a built-in template within AutoTableTop™ version 2.1's scenario selection screen, with no file downloads required to run it. The files above are provided for facilitators who want to review, customize, or run the exercise outside the platform.
How to Run This Exercise
Option 1 , Built-in template: Select "The FortiBleed Credential Compromise" from the AutoTableTop™ version 2.1 global scenario library and launch directly; the settings, network environment, and injects are pre-loaded.
Option 2, Downloadable files: Download the settings file above and upload it into a new AutoTableTop™ version 2.1 exercise, then use the Facilitator Guide and Participant Presentation to run a live-facilitated session, uploading the Incident Response Plan as a reference document for the platform to evaluate participant actions against.
Questions about running this exercise? Contact me at robert@threatgen.com.
© 2026 by Derezzed Inc. D/B/A ThreatGEN. AutoTableTop™ is a trademark and ThreatGEN® Red vs. Blue is a registered trademark of Derezzed Inc.